WordPress File Changes: Build a Useful Baseline
A file-change alert is useful only if you know what the original files looked like and what changed intentionally. WordPress core, themes and plugins all update regularly. Without a trusted baseline, routine maintenance can create noisy alerts that hide a genuine problem.
Start after a verified update
Before recording a baseline, confirm the site behaves normally. Check WordPress and plugin versions, review the latest approved changes and ensure your backup can be restored. If you suspect a compromise, investigate first rather than treating the current filesystem as trusted.
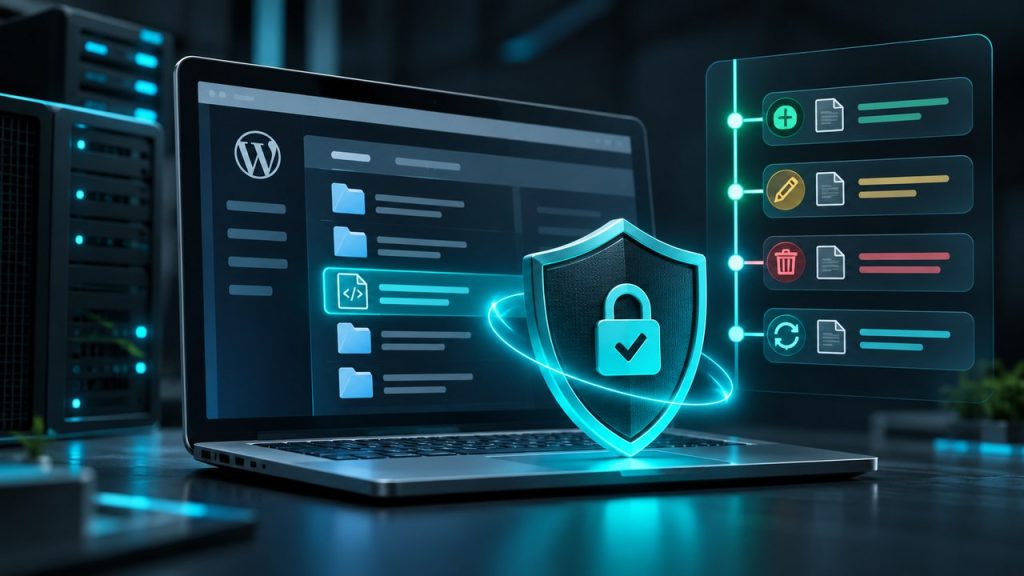
A file-integrity tool can calculate a cryptographic hash for each monitored file. A later scan compares those hashes. Different hashes indicate changed content; they do not, by themselves, establish malicious activity.
Document expected changes
Keep a simple change log: date, responsible person, component, previous and new version, and an explanation. When an alert occurs, compare the affected paths and times with the log. A verified plugin update is more likely to explain a changed plugin file than an unexplained modification late at night.
Prioritize suspicious paths
Look closely at unexpected executable files in upload directories, modified authentication-related code, unfamiliar administrator accounts and changes not associated with known maintenance. Investigate evidence in context; do not delete unfamiliar files without a backup and a recovery plan.
Rebuild the baseline deliberately
After approved updates are verified, capture a new baseline. Do not automatically accept every change as safe. A baseline is a reference point, not proof that a site is secure.
Pluginivo File Integrity Monitor PRO is designed to help track file changes using SHA-256 baselines and alerts. Combine it with least-privilege access, updates, tested backups and a documented response process.
Decide what an alert really means
An unexpected file-change alert is a starting point, not a diagnosis. Compare the alert timestamp with scheduled updates, deployments and administrator actions. Identify the exact path and whether the file was created, modified or deleted. If the change is unexplained, preserve a backup and investigate access logs before accepting a new baseline.
For a useful review routine, document the change, responsible person, business reason and decision. Never mark unknown changes as trusted merely to make the dashboard quiet. File Integrity Monitor reports differences from its baseline; it is not a malware scanner or firewall, and scheduled checks can depend on WP-Cron activity.
Next step: Explore File Integrity Monitor PRO on Pluginivo or review the product documentation. Plugin features support your workflow; results depend on your store configuration and data.